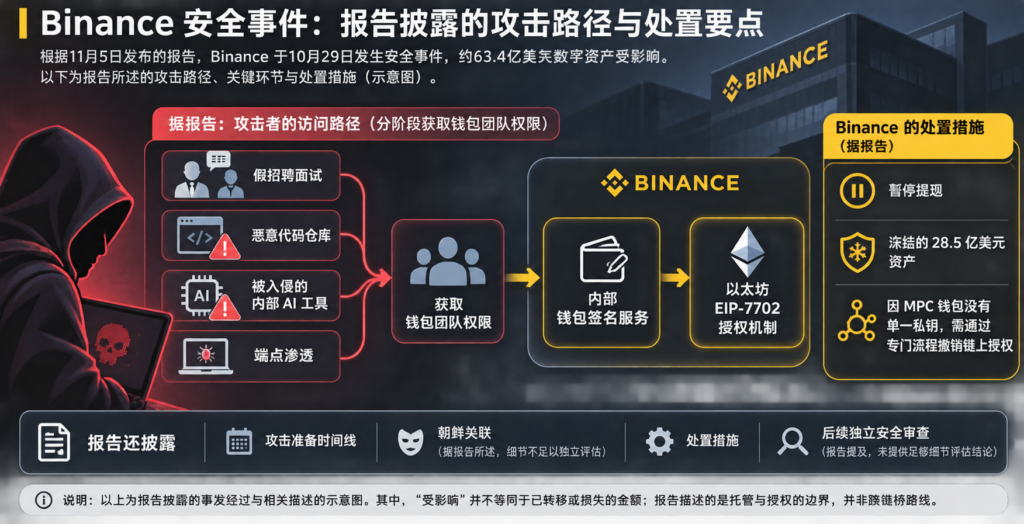
A report published on November 5, 2026, at 00:04:06 UTC+8 describes a Binance security incident on October 29 in which approximately $6.34 billion in digital assets was affected. “Affected” does not, by itself, establish how much was transferred or lost.
According to the report, the attackers gained access to the wallet team in stages through fake recruitment interviews, malicious code repositories, a compromised internal AI tool and endpoint infiltration. They then used an internal wallet-signing service and Ethereum’s EIP-7702 authorization mechanism to transfer assets. The account identifies a custody and authorization boundary—not a cross-chain bridge route.
Binance suspended withdrawals and froze approximately $2.85 billion in assets, the report says. It also says revoking the on-chain authorizations required a dedicated process because the MPC wallets did not have a single private key. The report describes an attack-preparation timeline, an alleged North Korea connection, response measures and a subsequent independent security review; the supplied account does not provide enough detail to independently assess that attribution or the review’s findings.